
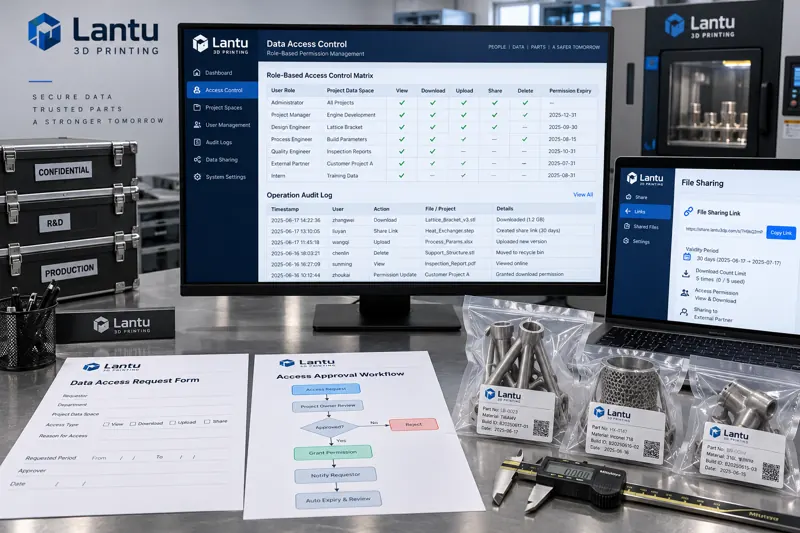
Introduction: A Mis-Sent File Reveals a Permission Problem, Not an Employee Problem
An additive manufacturing workshop received a customer complaint: a model file intended only for the person responsible for the project had been forwarded via a personal email account to an external industry peer by an employee who had already changed roles. During the review, the company found that three things were true at once—the employee's access to the old project had never been revoked after the transfer; file downloads required no approval; and the system had no record whatsoever of who downloaded which file and when. Together, these three failures turned an operation that could have been stopped into a data leak that could not be substantiated.
Such incidents are not uncommon in 3D printing companies. The industry tends to focus on encryption, confidentiality agreements, and watermarks, but what truly determines data boundaries is the account permission system: who can see what, who approved the access, and what traces the access left behind. Turning these rules into an executable engineering solution is more effective than signing ten more confidentiality agreements.
I. Why Permission Management Is More Difficult for 3D Printing Companies Than in General Manufacturing
The data formats used by 3D printing companies differ from those of mass-manufacturing enterprises, adding complexity to permission design. First, the data granularity is fine: a single part may simultaneously include six types of assets—an original 3D model, a repaired mesh file, a slicing file, a process parameter package, an inspection report, and photos of the physical item—and their sensitivity levels are not the same. Customers often authorize the use of a model for production only, without authorizing secondary modification or forwarding to third parties.
Second, there are many participants. In addition to internal design, process engineering, printing, post-processing, quality inspection, and delivery roles, there are outsourced processors, remote maintenance personnel from equipment manufacturers, customer-side drawing reviewers, and even third-party testing agencies temporarily involved in a project. Each type of external role requires a different data scope, validity period, and set of permitted actions. Attempting to cover them all with a single internal account system will inevitably result in loss of control.
Third, systems are fragmented. Model files reside on file servers or object storage, slicing parameters are held in local software from equipment vendors, inspection data is stored on standalone workstations for measuring instruments or CT equipment, and order information sits in business systems. Permissions are managed separately across four systems. When an employee changes roles, access must be modified in all four places, and missing any one of them leaves an exposure.
II. Role Definition: First Translate the Organizational Structure into Data Objects
The most common mistake in a permission system is to directly copy the organizational chart. Job positions are organizational concepts, while permissions are data concepts; a translation layer is required between them. A practical approach is to first establish a data object inventory, then define roles, and finally map job positions to roles.
Data objects should be organized by project rather than by department. A project directory should contain four subspaces: models, processes, inspections, and delivery. Each subspace should further distinguish among four actions: read-only, editable, downloadable, and externally shareable. Permissions defined in this way inherently contain project boundaries, preventing employees working on Project A from casually seeing files from Project B.
The number of roles should be controlled. As a rule of thumb, internal roles should be limited to six to eight: project manager, design engineer, process engineer, production operator, quality inspector, delivery staff, system administrator, and auditor. Too many roles make it impossible for anyone to remember what each role can do, eventually leading everyone to request administrator access. Auditors must be an independent role and must not have any data modification permissions; otherwise, they could delete logs themselves.
III. The Principle of Least Privilege: Deny by Default and Grant Temporary Access as Needed
Least privilege is not a slogan; it requires three verifiable rules. The first is deny by default: newly created accounts must not be able to see any project until explicitly authorized. Many systems are configured by default so that “all employees can read,” which in a 3D printing environment effectively makes customer models semi-public.
The second rule is that authorization must have an expiration date. Routine role permissions should be reviewed quarterly, project-based permissions should be tied to the project end date, and temporary external access should be precise to the day. Once permissions expire, the system should automatically revoke them and notify the project manager for confirmation, rather than relying on someone to remember to disable them. The third rule is separation of actions: downloading and external sharing are two separate permissions. Being able to download a file for production does not mean being able to send it externally; external sharing must be separately approved and recorded.
For highly sensitive data, dual authorization is recommended. Three types of operations should require a second person's review before execution: exporting original customer models, exporting an entire process parameter package, and bulk downloads exceeding a defined threshold. The value of the two-person rule is not merely to prevent malicious insiders, but to reduce the likelihood of single-person errors and leave a second witness after the fact.
IV. Account Lifecycle: Three-Stage Control for Onboarding, Role Changes, and Offboarding
Personnel changes are a common source of uncontrolled permissions. During onboarding, permissions should be managed through formal request records: the project manager submits the required data spaces and action list, an administrator configures the access after approval, and the configuration result is recorded back in the request as evidence. Verbal permission requests must be prohibited.
The role-change stage is the most critical and the most easily overlooked. The correct sequence is to revoke old-role permissions first and then grant new-role permissions, rather than stacking them. A more reliable practice is to freeze all project permissions on the day of the transfer, have the manager of the new role submit new authorization requests, and make all unrequested spaces inaccessible. If the employee still needs to participate in historical projects, access should be requested separately as a project member and assigned an end date.
During offboarding, three things must be completed on the same day: disable rather than delete the account, in order to preserve log associations; remove project membership in bulk; and invalidate all external sharing permissions and shared links. Deleting an account breaks the association to the actor in logs, making subsequent tracing impossible—an error many companies have already made.
V. Audit Trails: Logs Must Answer Five Questions
Audit trails are not created merely to store logs, but to reconstruct facts afterward. A qualified access log must at minimum answer: who, at what time, to which data object, performed what action, and with what result. In addition to user identifiers, timestamps, object identifiers, action types, and result statuses, the field design should record the source endpoint and network location to distinguish workshop-station access from abnormal remote access.
Logs themselves must be tamper-proof. Once written, they must not be modified or deleted, and administrator accounts must not have deletion permissions. The retention period must be no shorter than the dispute period stipulated in customer contracts, with more than twelve months generally recommended. Log files also require access auditing—who viewed the logs must itself be recorded.
Logs without review are equivalent to no logs at all. Three types of automated alerts are recommended: large-volume downloads outside working hours, daily downloads by a single account exceeding three times its historical baseline, and external accounts accessing unauthorized project spaces. An alert does not need to be immediately classified as a violation, but someone must handle it within a business day and leave a disposition record.
VI. Boundaries for External Accounts and Shared Links
Customer drawing reviewers, outsourced processors, and equipment manufacturer maintenance personnel should all use external accounts in separate namespaces and must not be mixed with the internal account system. By default, external accounts should access only explicitly shared objects, should not see the project directory structure, and should not be able to infer other file paths through links. Shared links should use non-enumerable random identifiers and be bound to an expiration date and maximum number of accesses.
Remote maintenance by equipment manufacturers is the channel most likely to be overlooked. Maintenance accounts typically have high-level privileges within equipment control systems. If those systems are connected to the production network's file system, it effectively gives outsiders a bypass around the permission system. The correct approach is to use a separate network channel for maintenance access, while ensuring that file export actions during maintenance are also subject to approval and audit trails.
VII. Implementation Checklist
Companies can conduct a self-assessment using the following questions: Do newly created accounts have no project visibility by default? Can you list all permissions currently held by a given employee within five minutes? Do all permissions have expiration dates? Does the role-change process involve stacked access by granting new permissions before reclaiming old ones? Are downloading and external sharing two independent permissions? Do logs include source endpoint fields and cannot be deleted? Are external accounts isolated from internal accounts? Are shared links bound to expiration dates and maximum access counts? Are external sharing links invalidated on the employee's last day? Was a permission review actually conducted in the previous quarter? If you cannot answer more than three of these ten questions, the permission system needs to be rebuilt.
Conclusion
The boundary of data assets at a 3D printing company is ultimately defined by its account permission system, not by encryption strength or confidentiality agreements. Translate job positions into roles, bind roles to time-limited data objects, set the default policy to deny, and make every access event an auditable record. If these four steps are implemented properly, the vast majority of data leaks can be stopped before they occur or clearly substantiated afterward. Permission management is not a one-time policy release, but an engineering mechanism that requires quarterly reviews and continuous refinement as projects change.
Invia un modello, un disegno, un'immagine o note scritte. Gli ingegneri valuteranno materiale, processo, finitura e consegna in base all'uso effettivo.