
Introduction: One Alarm, Three Shifts, Three Responses
A metal powder bed fusion machine repeatedly displays a “high oxygen content” alert during the night shift: Team A continues printing based on experience, Team B stops the machine and purges the chamber again, and Team C simply resets the alarm. All three records describe the same phenomenon, yet none can answer: “Which event code does this alert correspond to? What is the trigger threshold? Is it permissible to continue the build? Is re-verification required after reset?” When lantu3D undertakes lifecycle projects spanning design blueprints through physical delivery, it finds that shops often lack neither sensors nor inspection checklists. What they lack is a controlled code table that translates raw events generated by equipment controllers into actionable decisions. This article is not about how to repair equipment, but rather an upstream layer: how alarm and event codes themselves are numbered, classified, linked to interlock actions, controlled for suppression and reset, and frozen with firmware versions, so that the same event receives the same response on every shift.
I. Define the Boundaries First: Alarm Codes, Fault Symptoms, and Quality Events Do Not Belong in One Table
First, separate three objects that are easily confused. An alarm code is a structured identifier output bitwise or wordwise by an equipment control system; its meaning is defined by the code table and must be unique, stable, and machine-readable. A fault symptom is an operator-observed description, such as “streaks in powder spreading”; it is natural language, and multiple symptoms may point to the same code. A quality event is a post-event determination of impact on the part, such as “this build is quarantined pending inspection”; it belongs to the release-decision layer. Previously discussed three-level power-quality measurement points and waveform records, predictive-maintenance mappings of failure modes to monitoring indicators and thresholds, and three-state equipment inspection classifications of normal/abnormal/reinspection all consume a type of event to make another decision. They do not define “where a code comes from, how code domains are divided, or what happens to old records after a code changes.” The key question for determining the layer is: Does this document explain “how to calculate a conclusion after receiving a signal,” or “what the signal is called when it is generated, what level it belongs to, and what actions it may trigger”? Only content that can be reduced to “one code, one classification table, one interlock rule, and one version-freeze record” belongs to the code-table engineering layer.
II. Code-Domain Classification: Give Every Event a Permanent, Never-Reused Identity
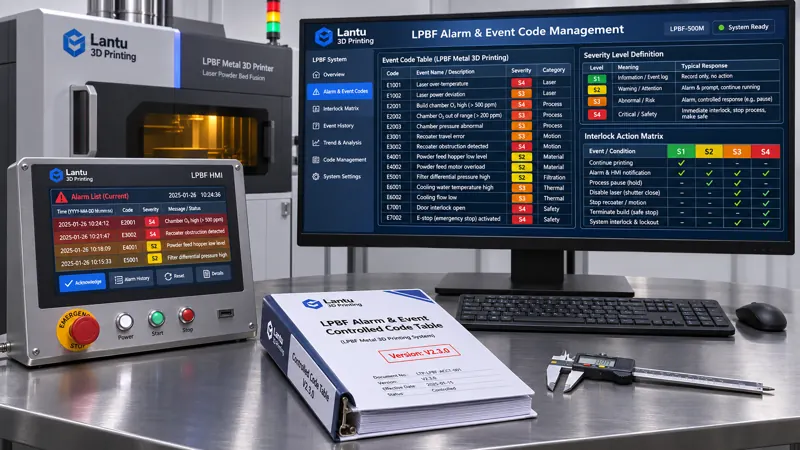
A fixed-length five-segment code is recommended: E-<equipment family, 2 digits>-<subsystem, 2 digits>-<sequence number, 3 digits>-<severity, 1 digit>. For example, LP-GS-0217-3 represents event No. 217 for the recoating/gas subsystem, with severity level 3. Equipment families are divided by process platform (LP for laser powder bed fusion, BJ for binder jetting, PJ for photopolymerization, and DE for directed energy deposition), while subsystems are divided by functional domain (GS for gas circuit and oxygen content, RC for recoating and blade, LS for laser and optics, TH for build-plate preheating, MT for motion and servo systems, PW for power supply and utilities, and CT for control and communications). For every code, the code table should define at least eight fields: unique code, standard Chinese and English descriptions, trigger-condition expression, default severity, default interlock action, permitted operating states, firmware version in which it first became effective, and responsible response role. Once assigned, a sequence number must never be reused. Retired events should only be marked deprecated while retaining historical mappings. An old number must never be assigned a new meaning; otherwise, a quality record from three years ago could be interpreted as an entirely different event during retrospective review.
III. Severity and Interlocks: A Four-State Action Matrix from “Notification” to “Safety Shutdown”
Four severity levels are recommended, with each level bound to one default action to prevent discretionary on-site decisions: S1 notification (write to the event log only, without interrupting the build, such as a reminder that filter differential pressure is approaching the replacement limit); S2 warning (continue the build but reduce speed or apply a marker, such as when chamber oxygen reaches the 800–1000 ppm range, automatically extending interlayer gas purging and marking the affected layer); S3 process hold (pause recoating while retaining the current layer number and inert atmosphere, such as oxygen content >1000 ppm for ≥2 s or measured laser power deviating from the setpoint by ±8% for more than 3 layers); before resuming, fusion quality must be reviewed for the three layers above and below the affected layer; and S4 safety shutdown (disable laser output, maintain gas circulation, and immediately quarantine the build, such as in the event of protective-gas interruption, chamber-door interlock activation, or emergency-stop circuit actuation). Automatic reset and suppression are always prohibited for S4. The action matrix should be defined in six columns: “severity → interruption required → atmosphere retained → build quarantine required → first-off re-verification required → notified role,” and released after joint approval by process, equipment, and quality functions.
IV. Debounce, Trigger Conditions, and Evidence Snapshots: Make Every Event Reproducible
Trigger conditions cannot simply state “high oxygen content”; they must be expressed reproducibly as: measured value / comparison operator / threshold / duration / hysteresis band / enabled operating state. For example, oxygen content may use a 1000 ppm threshold, a duration of 2 s, and a 5% hysteresis band, clearing only after the value falls below 950 ppm. It is enabled only during build and preheating states, and is not evaluated during standby or maintenance. Laser-power deviation may use ±8% over three consecutive layers, with debounce based on a 100 ms sampling period; confirmation occurs only after the condition is true for three consecutive cycles, while transient spikes of <50 ms are recorded as transient events and do not escalate. Each confirmed event should generate an evidence snapshot with ten fixed fields: event code, timestamp (synchronized to the equipment clock, with drift ≤1 s), current layer number, actual laser power, recoater-axis position, oxygen content and dew point, parameter-package hash, code-table version, firmware version, and operator ID. Key waveform data for 200 ms before and 1 s after the event must also be retained. Without this snapshot, the event impact boundary cannot be determined afterward, and S3/S4 release decisions have no evidentiary basis.
V. Suppression, Reset, and Temporary Bypass: Put Exceptions Inside an Authorization Cage
Legitimate on-site suppression needs do exist, such as during oxygen-analyzer calibration, but they must be controlled through engineering constraints: suppression is permitted only for S1–S3, while S4 is permanently prohibited; the request form must state the code number, reason, alternative monitoring method, and validity period; the validity period should be ≤8 hours or ≤1 build, whichever comes first, with automatic expiration; execution requires dual authorization by equipment and quality personnel; and during suppression, all events must still be recorded, with only suppressed=true and the authorization document number added. Events must never be silently discarded. Reset is likewise not just pressing a button: before resetting an S3/S4 event, the root-cause code, corresponding to an entry in the fault dictionary, and the person performing the corrective action must be recorded. After reset, a first-off standard specimen verification must be performed, and the three layers above and below the event layer must be checked for lack of fusion and porosity. Build quarantine may be lifted only when all four records are complete. It is recommended to include “suppression rate ≤1% of builds,” “uncategorized-event proportion ≤2%,” “more than five repetitions of the same root cause within one hour automatically generates a root-cause work order,” and “event-to-snapshot completeness ≥99%” in the monthly dashboard.
VI. Version Freezing and Change Control: Where Do Legacy Codes Go After a Firmware Upgrade?
A code table is a controlled document, not an Excel file that can be edited casually. Each release should generate a version number, SHA-256 hash, effective date, applicable equipment serial-number list, and minimum firmware version. These should be written into the delivery evidence chain through a three-key association with the parameter-package version and build number. Adding or revising a code must follow a change request: impact analysis (which historical records, work instructions, and interlock logic are affected) → three-party review → old-to-new code mapping → effective-date switchover → retirement of old work instructions. A code-table consistency comparison must be performed before and after a firmware upgrade: verify item by item that the codes, severity levels, and descriptions actually output by the controller match the current controlled version. If they do not match, production release must be frozen. Historical code tables and event logs should be retained for no less than the product lifetime plus three years and archived in read-only form.
VII. Implementation Checklist and Common Pitfalls
Implementation can proceed over 30 days: in Week 1, export the complete controller-event list, renumber it using the five-segment structure, and establish a code-domain register; in Week 2, complete the four-level action matrix and trigger-condition expressions, adding debounce and hysteresis bands; in Week 3, establish automatic links between the ten event-snapshot fields, parameter-package hash, and layer number; and in Week 4, conduct a 30-minute retrospective drill—randomly select an S3 event from three months earlier and require reconstruction of the code-table version, trigger conditions, snapshot, and release conclusion at that time, with a reconstruction success target of ≥95%. There are four common pitfalls: writing alarm codes as natural-language descriptions, making them unreadable by machines; defining thresholds without duration or enabled operating states, causing maintenance-state false alarms to flood the system; stopping event recording during suppression, breaking the evidence chain afterward; and continuing to use an old code table after a firmware upgrade, causing old and new meanings to become confused.
Conclusion
The controlled definition of equipment alarms and event codes is the foundational engineering layer that translates “what the machine says” into “what the shop should do.” It does not replace energy-consumption accounting, power-quality management, predictive maintenance, or inspection-lot management; rather, it provides those methods with a stable, reproducible, and traceable input dictionary. For platforms spanning the full chain from design and process development through manufacturing and physical delivery, only by making every code unique, every severity action unique, every exception traceable, and every version freezable can a notification during the night shift become an engineering fact that leads to the same conclusion on every shift.
Submit a model, drawing, image or written notes. Engineers will review material, process, finishing and delivery based on actual use.